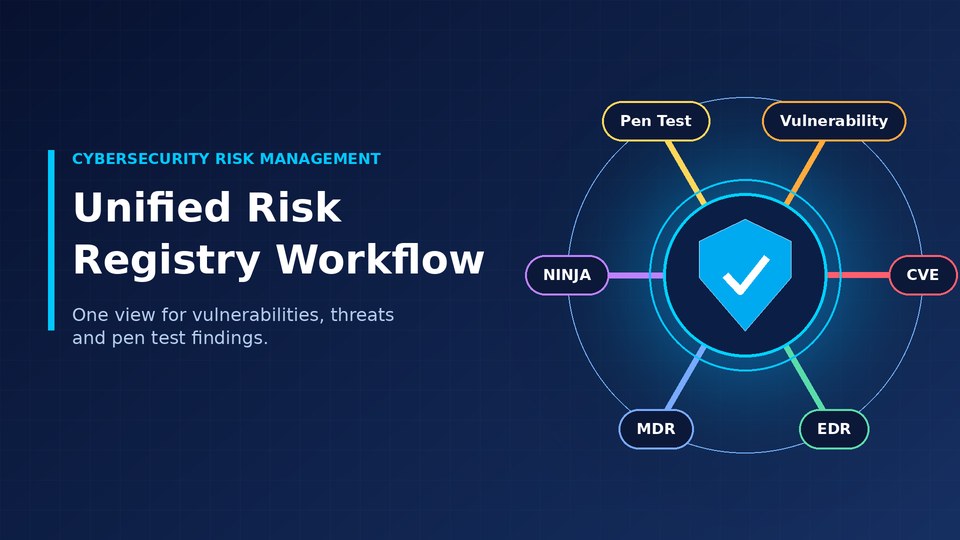
Modern organizations use multiple cybersecurity tools to identify vulnerabilities, detect threats, monitor endpoints, and assess security risks. However, security teams often face a common challenge: vulnerability, CVE, EDR, MDR, NINJA, and penetration testing data is spread across different platforms. Without a unified workflow, important findings can be difficult to prioritize, assign, remediate, and track.
A centralized Risk Registry can address this challenge by bringing security findings from multiple sources into one structured and actionable workflow.
Centralize Security Data in One Risk Registry
The first step is creating a centralized Risk Registry capable of collecting and organizing information from different cybersecurity solutions. Instead of reviewing separate dashboards for vulnerability scans, endpoint detection, MDR, NINJA assessments, and penetration tests, security teams can manage relevant findings through a single interface.
Storage Guardian’s Risk Registry will incorporate these security data sources directly into the DR Runbook Portal, providing a user-friendly UI where security teams can view, manage, and track identified risks.
Each risk record can include important information such as the affected asset, vulnerability or issue, severity, source, date identified, assignee, remediation status, and supporting evidence.
Integrate Vulnerability and CVE Data
Vulnerability management should be a core component of the Risk Registry. Vulnerability scanners identify weaknesses across systems, while Common Vulnerabilities and Exposures (CVE) information provides standardized identifiers and additional technical context.
By integrating CVE and vulnerability data into Storage Guardian’s Risk Registry, security teams can connect vulnerabilities to specific assets and remediation activities. This makes it easier to identify recurring issues and prioritize remediation based on severity, exposure, and business impact.
Incorporate EDR and MDR Findings
Endpoint Detection and Response (EDR) provides visibility into suspicious endpoint activity, while Managed Detection and Response (MDR) provides continuous monitoring and threat detection.
Bringing EDR and MDR findings into the Risk Registry allows security teams to correlate security events with existing vulnerabilities and affected assets. A security alert can therefore become an actionable risk record rather than remaining isolated within a separate monitoring platform.
Add NINJA and Penetration Testing Results
NINJA security assessment data and penetration testing results provide additional insight into an organization's security posture. Penetration testing can validate whether identified weaknesses are potentially exploitable and reveal security gaps that automated vulnerability scans may not identify.
With Storage Guardian’s Risk Registry, these findings can be incorporated into the DR Runbook Portal and managed alongside vulnerability, CVE, EDR, and MDR information.
Assign Owners and Define Remediation Strategies
Identifying a risk is only the beginning. An effective Risk Registry must make it easy to take action.
Storage Guardian’s Risk Registry will provide dedicated Assignee and Remediation Strategy fields, allowing organizations to identify who is responsible for addressing each finding and document the planned approach for remediation.
A standardized workflow can move findings through stages such as:
Unassigned → Assigned → In Progress → Fixed → Verified
This creates clear accountability and provides security teams with visibility into the status of outstanding risks.
A User-Friendly DR Runbook Experience
Integrating Risk Registry capabilities into the Storage Guardian DR Runbook Portal provides security teams with a centralized and user-friendly experience for managing cybersecurity risks.
Rather than switching between multiple security platforms and manually compiling reports, teams can use the portal to review findings, assign responsibilities, document remediation strategies, track progress, and maintain evidence for security and compliance activities.
Build a Unified View of Cybersecurity Risk
Integrating vulnerability, CVE, EDR, MDR, NINJA, and penetration testing data transforms individual security findings into a structured cybersecurity risk management workflow.
With Storage Guardian’s Risk Registry incorporated into the DR Runbook Portal, organizations can centralize security information through a user-friendly interface while maintaining clear assignees, remediation strategies, statuses, and accountability.
The result is a more organized approach to identifying, managing, remediating, and continuously monitoring cybersecurity risks—all within a unified workflow.


